Network connections
Since v0.17.0 the agent shows what each workload is connected to, right now and over the last days. It only reads: nothing on this page changes traffic, the firewall or system settings.
Where to look
Section titled “Where to look”| Tab | Permission | Shows |
|---|---|---|
| Server → Network | network.view |
Every workload on the server: connections, listeners, talks-to, conntrack, latency to private-network peers, WireGuard peers |
| Site → Network | telemetry.view |
The site’s containers (or its native processes), per compose service, with its listeners, talks-to and inbound clients |
| Database → Network | databases.view |
The instance’s connected clients (named sites and servers) and connection counts |
What you see
Section titled “What you see”- Connections by state and direction: established, SYN sent / received, FIN wait, TIME_WAIT, CLOSE_WAIT and the rest, inbound and outbound.
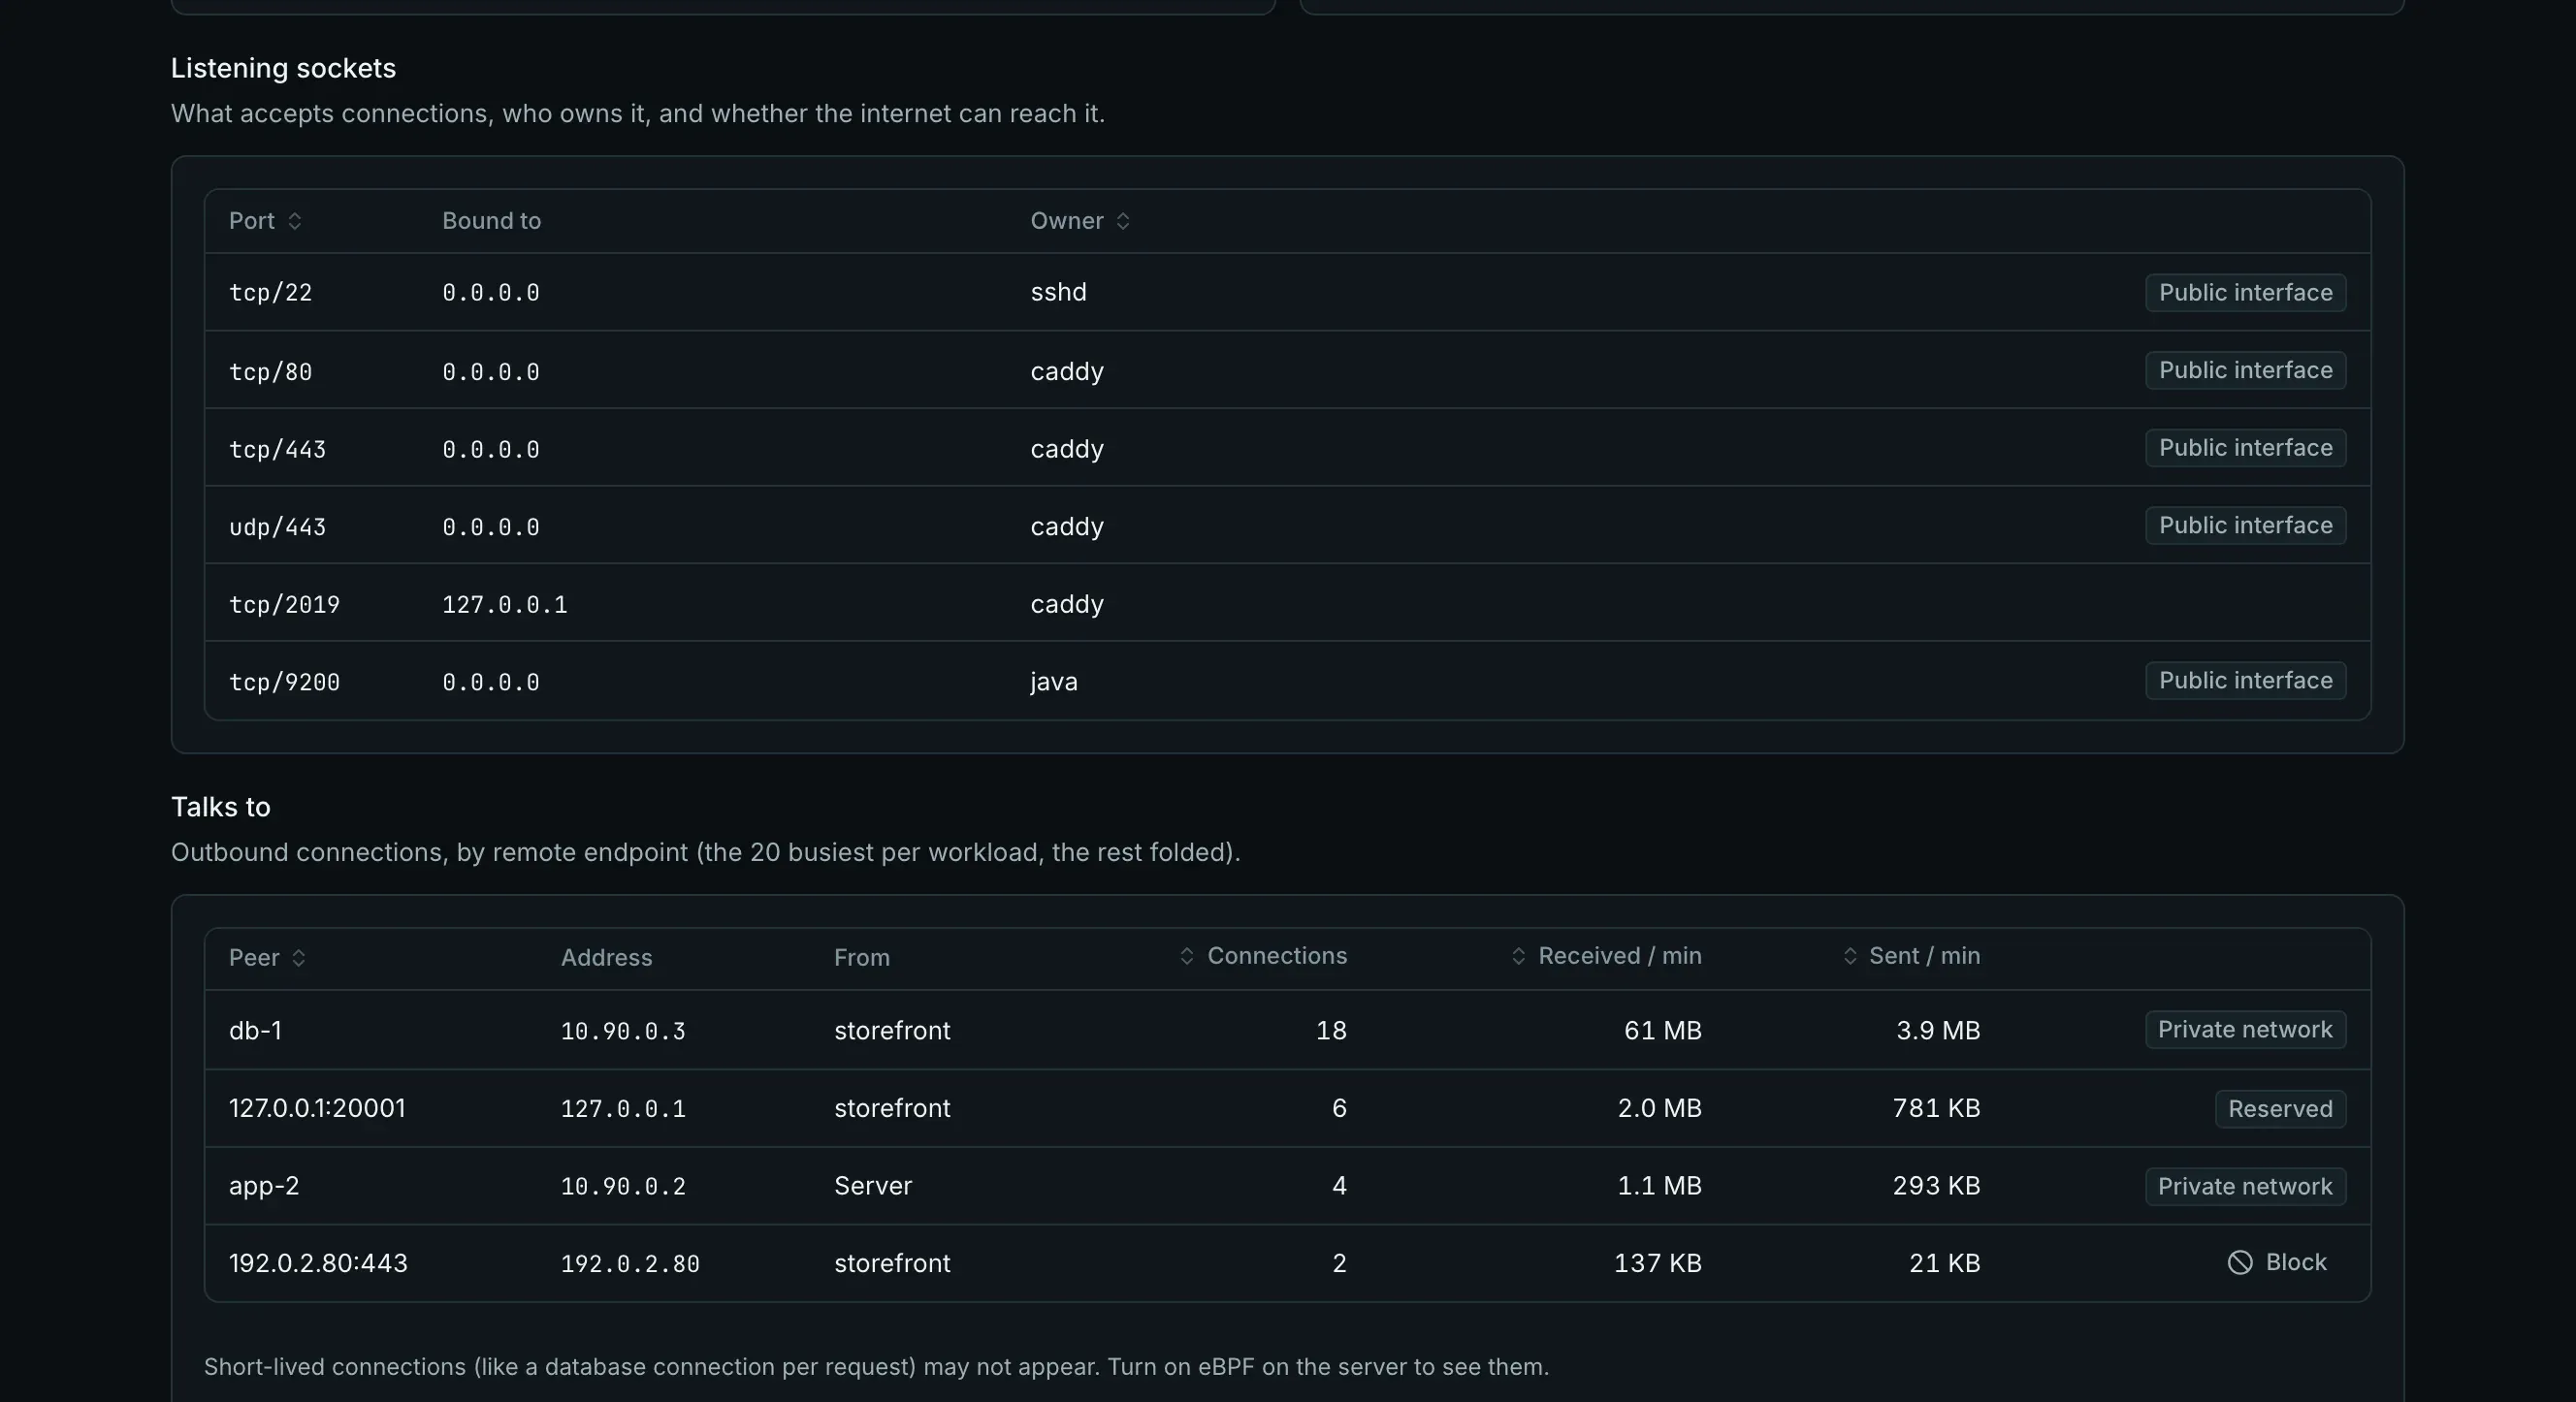
- Listening ports with the site, container or process that owns each one, and whether it is public (bound to a wildcard or a public address) or private.
- Talks to: the top 20 peers per workload in each direction, with connection counts and, when the kernel counts them, bytes. Peers are named after your servers, databases and sites where possible; other public addresses show their reverse DNS name.
- Long-lived connections, such as WebSockets, server-sent events and long polling: inbound connections open for at least 60 seconds.
- Conntrack table usage against its limit.
- Latency between servers that share a private network, and WireGuard peer health (last handshake, bytes, latency).
Bytes per peer
Section titled “Bytes per peer”Sockets carry no byte counters; the kernel’s connection tracking does, when accounting is on. It is off by default on most kernels and Falak never turns it on itself. Without it, peers show connection counts only, and the server’s Network tab explains how to enable it:
echo net.netfilter.nf_conntrack_acct=1 | sudo tee /etc/sysctl.d/90-conntrack-acct.confsudo sysctl -w net.netfilter.nf_conntrack_acct=1Only connections opened after that have counters, and connections that last less than a minute are partly missed.
How the numbers are measured
Section titled “How the numbers are measured”- Each container is read in its own network namespace; native sites are matched to their processes’ sockets.
- Latency probes between servers connect to a closed port on the peer’s private address and time the refusal. The agent never probes database ports, so nothing shows up in SSH or database logs.
- Long-lived connections are counted from when the agent first saw them (to within 15 s).
- Client and peer addresses stay in the control plane (the latest report per server); they are never metric labels.
Exposed-ports audit
Section titled “Exposed-ports audit”A public listener on a server is exposed when it is reachable from anywhere and Falak doesn’t expose it on purpose: the firewall isn’t applied, a rule accepts the port from anywhere, or it is a container’s published port. The edge (80/443), SSH, the WireGuard ports and a database’s port with a public-access allowlist are expected.
Each exposed port becomes a security Issue in Insights, such as PostgreSQL 5432 reachable from the internet, and resolves itself once the port is closed, rebound to a private address or dropped by the firewall.
Alerts
Section titled “Alerts”These join the Network area of the default rule pack (all warnings):
| Type | When |
|---|---|
network.conntrack_full |
Conntrack at 85 % of its limit for 5 minutes |
network.exposed_port |
A port became exposed (recovers when it no longer is) |
network.wireguard_stale |
A peer’s last handshake is older than 5 minutes, held 5 minutes |
network.latency_spike |
A probe fails, or its latency is at least 3× its baseline (and 50 ms above it), held 5 minutes |
Metrics
Section titled “Metrics”| Metric | Meaning |
|---|---|
falak_net_connections |
Connections by falak_net_state and falak_net_direction |
falak_net_connections_long_lived |
Long-lived inbound connections |
falak_net_listeners |
Listeners by transport and exposure |
falak_net_peer_connections, falak_net_peer_io_bytes_total |
Per named peer (falak_net_peer) |
falak_net_conntrack_entries, falak_net_conntrack_limit |
Conntrack usage |
falak_net_probe_connect_time_seconds, falak_net_probe_up |
Latency probes |
falak_net_wireguard_handshake_age_seconds, falak_net_wireguard_io_bytes_total |
WireGuard peers |